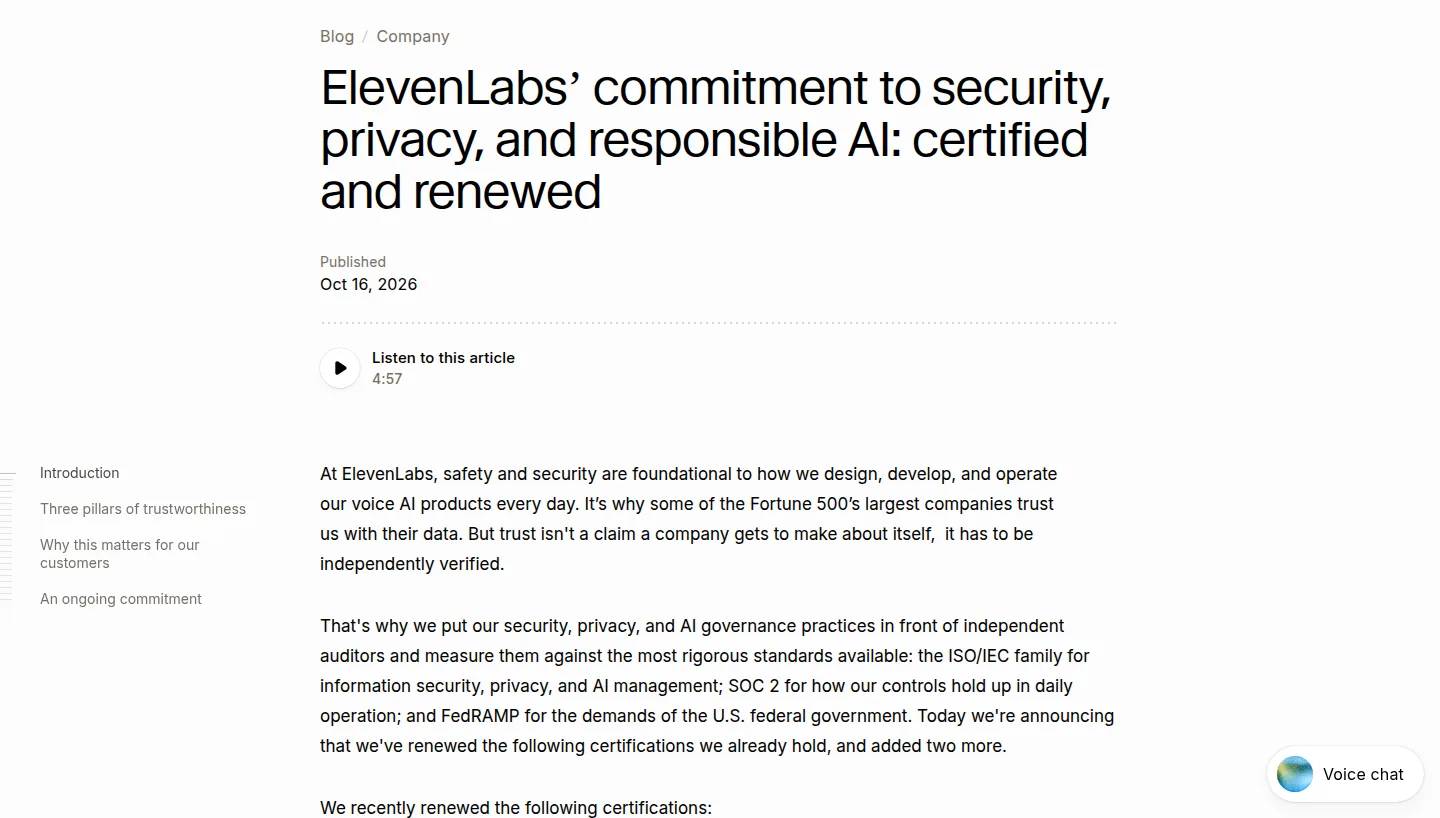
ElevenLabs published a company post on October 16, 2026 listing the security, privacy and AI management certifications it renewed, and two it added. The entry that matters commercially is FedRAMP 20x Class A, the route into the U.S. federal market. No product shipped with the announcement, no rate changed, and the post is a compliance update rather than a launch.
What was actually released
Seven renewal lines and two additions, all listed in the same post. The renewals keep certifications the company already held: ISO/IEC 27001:2022 for information security management, ISO 27701:2019 for privacy information management, ISO/IEC 42001:2023 for AI management systems, ISO 27017 and 27018 for cloud-specific controls, SOC 2 Type II as an attestation over the past year of operation, PCI DSS Level 1 Service Provider for payment data, and the UK Cyber Essentials and Cyber Essentials Plus scheme.
The two additions are narrower than the headline suggests. SOC 2 Type I is issued for ElevenProductions, which is one product line named explicitly in the post. FedRAMP 20x Class A is the second addition, and the post points to the company’s listing on the FedRAMP Marketplace rather than to an authorization letter.
| Document | Status in the post | What it actually certifies |
|---|---|---|
| ISO/IEC 27001:2022 | Renewed | Information security management system |
| ISO 27701:2019 | Renewed | Privacy information management, as an extension of 27001 |
| ISO/IEC 42001:2023 | Renewed | AI management system, meaning process, not model quality |
| ISO 27017 and 27018 | Renewed | Cloud security controls and personal data held in the cloud |
| SOC 2 Type II | Renewed | Controls designed and operating over a period |
| PCI DSS Level 1 Service Provider | Renewed | Controls around payment card data |
| Cyber Essentials and Cyber Essentials Plus | Renewed | UK government-backed baseline controls |
| SOC 2 Type I | Added, ElevenProductions only | Controls designed as of a single point in time |
| FedRAMP 20x Class A | Added | Entry certification for the federal marketplace |
Read on the ElevenLabs post of October 16, 2026. The scope column is the post’s own description of each standard, not a product map: the post does not publish a matrix saying which certification covers which product line.
What the claim rests on
Each document listed is an independent assessment, and that part is not in dispute: an accredited auditor issued the ISO certificates, and an accountant attested SOC 2. What the post does not carry is the evidence underneath. No audit period is given, no auditor is named, no report is attached, and the compliance page it links to is the company’s own summary. For a buyer, this is a pointer, not a document.
The FedRAMP entry deserves the closer read, because the name carries more weight than the class. The post itself describes it as the new entry pathway under FedRAMP 20x. The program’s own rules put Class A at the bottom of a four-step scale, meant for cloud services that already run mature programs and want to enter the federal marketplace, with a small amount of information submitted in advance and a small subset of initial monitoring and reporting. Class B covers low-impact services, Class C covers moderate-impact services, and Class D, the high-impact tier, is still listed as a future phase.
That ordering is the substance of the claim. Class A is a door into the federal market, not a clearance for sensitive workloads. An agency looking for a service to handle controlled data will be reading for Class C or D, and neither is what this announcement delivers.
What the certifications do not measure
An ISO 42001 certificate says the company has auditable processes for building and operating AI. A SOC 2 Type II report says controls operated over a review period. Neither says a cloned voice is accurate, that a generated voice cannot be misused, or that the model performs on your audio. Those remain procurement questions with no certificate attached.
The SOC 2 addition is the other place where a careful reader slows down. Type I attests to the design of controls at a single moment; Type II attests that they operated over a period. Adding a Type I for one product line, while renewing a Type II for the organization, means the newest scope has the weaker of the two opinions. Normal for a new product, and the sentence that disappears when the list is repeated.
What the post does not publish
No audit dates, no auditor names, no report access path beyond a request to the security assurance team, no product-by-product scope matrix, and no statement on where customer audio is stored. Data residency, the question that decides most enterprise voice deals, is absent from the page.
On this page
What it changes for teams buying voice AI in the U.S.
For anyone answering a security questionnaire, this shortens the first round. ISO 27001, SOC 2 and PCI DSS are the three boxes that appear in almost every vendor review, and having them renewed rather than expired removes the follow-up email that stalls a pilot for a week.
The FedRAMP entry changes a narrower thing. It puts the company in the federal marketplace at the lowest tier, which is enough to start conversations with agencies about low-impact uses: a public-facing information line, a demo, an internal tool that handles no controlled data. It is not enough for a benefits system or a case file, nor for anything an agency classifies as moderate or high impact.
Two questions are worth asking before the list is accepted at face value. First, which products sit inside the audited boundary: the post names ElevenProductions once, and describes every other document as organizational. Second, what the report says, since a SOC 2 Type II carries exceptions, and the exceptions are where the useful information sits.
FedRAMP is how the U.S. government decides which cloud services it will trust with federal data, and it’s among the most demanding assessments in the industry.
The Neural Minute take
Certification posts have become the most common press release in AI, because procurement teams ask for them. That makes this a real signal, just not the one the headline offers. The news is not that ElevenLabs is certified; it is which rung of FedRAMP it reached, and the post is careful enough to name the class rather than write “FedRAMP certified” and stop there.
Our reservation is about the map. We have covered ElevenLabs twice this month, once on the voice agent product and once on its detection of AI callers, and in both cases the question that mattered was scope: what the product does on a real call, in a real accent, under a real consent regime. A compliance page cannot answer that, and nine documents give the impression of a perimeter without drawing one. Take the certifications as a reason to skip the first email, then spend the saved time on the two questions that decide the deal: is my product inside the boundary, and where does my audio live.
Sources
- ElevenLabs, “ElevenLabs’ commitment to security, privacy, and responsible AI: certified and renewed”, published October 16, 2026: https://elevenlabs.io/blog/certification-renewals
- The renewed and added certifications, read on the same page on October 17, 2026, including the FedRAMP 20x Class A description and the SOC 2 Type I scope
- FedRAMP 20x class definitions, read on the program’s own 20x page on October 17, 2026: Class A for services entering the federal marketplace, Class B for low impact, Class C for moderate impact, Class D a future phase
- Prior Neural Minute coverage of the vendor: the voice agents launch and the AI caller detection